


Endpoint Management with Microsoft Intune
Intune & Endpoint News 2026
On this page
Introduction
Microsoft put a lot on the table again this year. Between new agent platforms, a generous round of Intune licensing changes and some serious Entra ID additions, the first half of 2026 gave us plenty to digest.
TL;DR
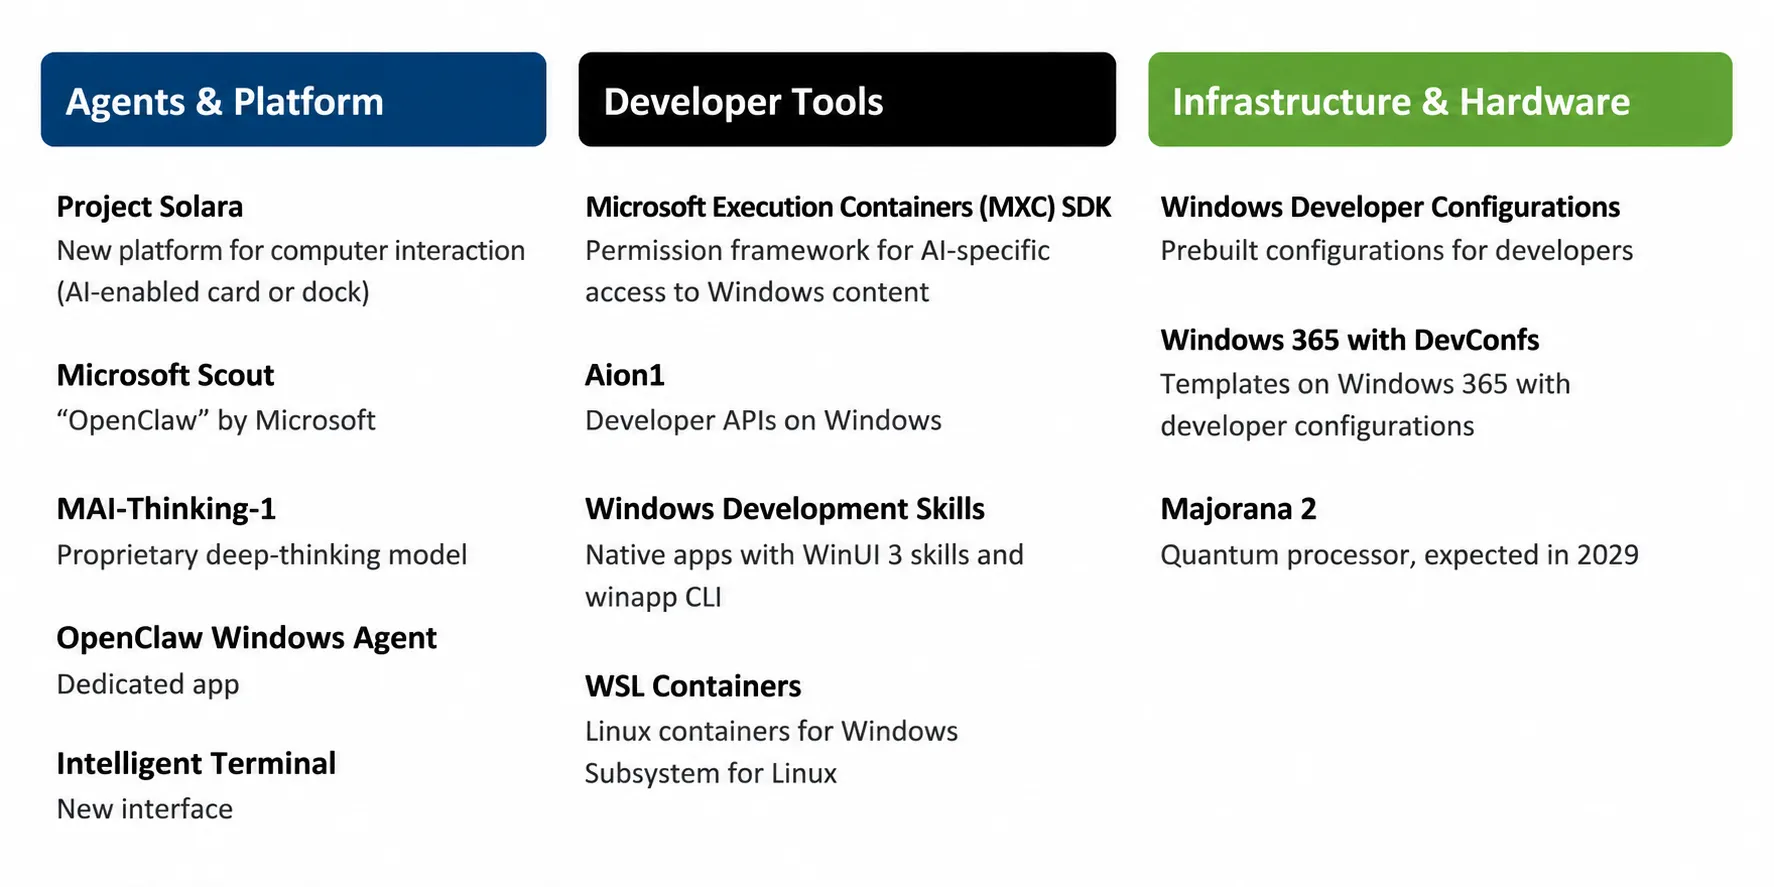
- Microsoft is building Windows into an agent platform - Project Solara, Microsoft Scout and an OpenClaw Windows Agent point the way
- Intune licensing got more generus — several former add-ons are now bundled into Microsoft 365 E3/E5.
- Maintenance Windows finally let you define exactly when updates and reboots happen
- Multi Admin Approval now covers Compliance and Configuration policies
- Authenticator vulnerability (CVE-2026-41615, CVSS 9.6) - update now
- Entra added Backup & Recovery, Tenant Governance, the Tenant Configuration API and Agent ID
- Entra Connect Sync: be on 2.5.79.0 before 30 September 2026 or sync stops ⚠️
Project Solara and Microsoft Scout
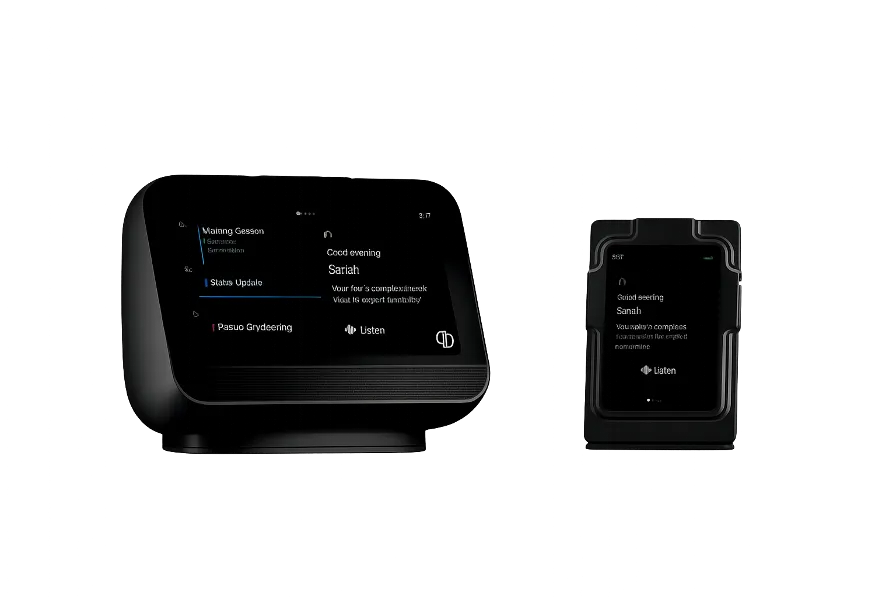
- Project Solara: a new platform for computer interaction, designed around AI-enabled hardware (think an AI-enabled chip card or stand). It's the foundation for how people and agents will interact with the machine.
- Microsoft Scout: Microsoft's own take in the "OpenClaw" space. This is Microsoft's agent concept for operating a computer the way a person would.
- OpenClaw Windows Agent: a dedicated app that lets that agent actually work on Windows.
Intune
What's New in Intune (2026 H1)
The full list for the half. Flags mark what to watch:
🏴 Recommendation · ‼️ Disruption · ⚠️ Needs action · 💡 Especially relevant
- PowerShell script installer for Win32 apps 🏴
- Admin Tasks now GA
- Feature Update Report support for 25H2
- New firewall network endpoints ‼️
- More options for assignment filters for managed apps on mobile
- Filter by Android management mode in the settings catalog
- New supported OEMConfig apps
- New settings in the Windows settings catalog
- New MAM apps
- Lenovo Device Orchestration link in the admin center
- EPM support on AVD
- Updates to operators in device query for multiple devices
- Autopatch update readiness
- Ending support for legacy Apple MDM software update policies ‼️
- Multi Admin Approval for Compliance and Configuration policies 🏴
- New setting control for MDM enrollment and account registration
- New updates to the Apple settings catalog
- Apple DDM supports assignment filters
- Improved Remote Help update reporting on macOS
- Guided scenarios removed from the Intune admin center
- Scoped permissions for RBAC
- Proxy support for Advanced Analytics on clients
- Support Assistant access expanded to all authenticated users
- Hotpatching default enablement ‼️
- Intune security baseline for Windows 11 version 25H2
- Support for Red Hat Enterprise Linux 9 and later
- Remote Help connectivity update ‼️
- Recovery lock features for macOS
- DDM for LOB apps on Apple mobile
- New TeamViewer connector experience
- Support for Android XR devices
- Intune Data Warehouse connector retirement in Power BI ‼️
- New reporting considerations for compliance policies
- Change Review Agent suggestions in Multi Admin Approval
- Direct LOB Android app management 🏴
- Updated security baseline for Edge v139
- Autopatch update risk visibility report
- Updated minimum version of IME
- New remote actions on Managed Home Screen on Android
- New device page 🏴
- Support for Ubuntu 26.04 LTS
- Support for userless ADE for visionOS and tvOS devices
- Access management for Apple services
- Expanded support for EPM requests
- Enhanced app inventory with faster data updates 🏴
- Complete Platform SSO during ADE 🏴
- Intune RBAC roles with access to Copilot in Intune
In Development for Intune
- Scope tags support for EPM reports
- Multiple managed accounts for MAM 💡
- Disable MAC address randomization on macOS Wi-Fi profiles
- New Wired Networks device config profile
- New Block Bluetooth sharing on Android settings catalog
- Enrollment time grouping for ADE GA
- Agentic identity for Policy Config Agent
- Strict Tunnel Mode on Android
- Security Baseline for audits of STIG 💡
- Support for Device Control policy managed by Sense
- In-place renewal of Cloud PKI issuing CAs
- Custom compliance settings for macOS
- Client-driven compliance evaluation 💡
- Controlled Configuration for MDAV
- New reporting considerations for compliance policies 💡
- Update to the latest Company Portal Intune App SDK
- New network endpoints
- Support statement for Windows 10 in Intune
- Intune moving support to iOS/iPadOS 17 and later & macOS 14 ⚠️
- New Intune connector for hybrid join ⚠️
- Strong mapping for SCEP and PKCS certs
Windows 365
Project Opal brings a Computer-Using Agent to the Cloud PC - it uses Copilot & WorkIQ and runs on Windows 365. Currently limited to Edge and hosted in Dublin. I wrote the full setup in my post:
Also: Frontline is now just called Flex (same product), and Bare Metal Recovery for Windows 365 Link has arrived.
powered by Oceanleaf
Related posts

