M365 security landscape
In mid 2021, Microsoft offers a lot of security oriented products and services in their cloud portfolio. But what are they capable of? Where do they even take place or protect you? I want to explain this landscape to you, mention some real world intentions and talk about their relationship to each other.
If you are new to this field, it may be helpful to understand the content of my previous posts:
The landscape
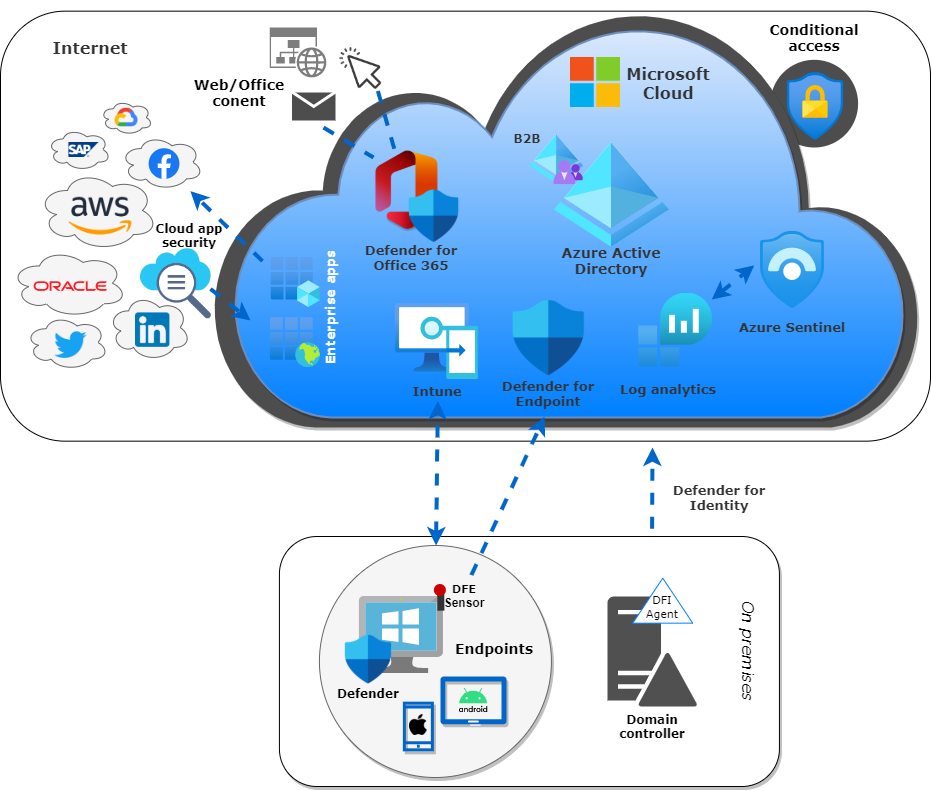
We focus on three areas: the on premises environment, your Microsoft tenant, and the Internet.
On premises
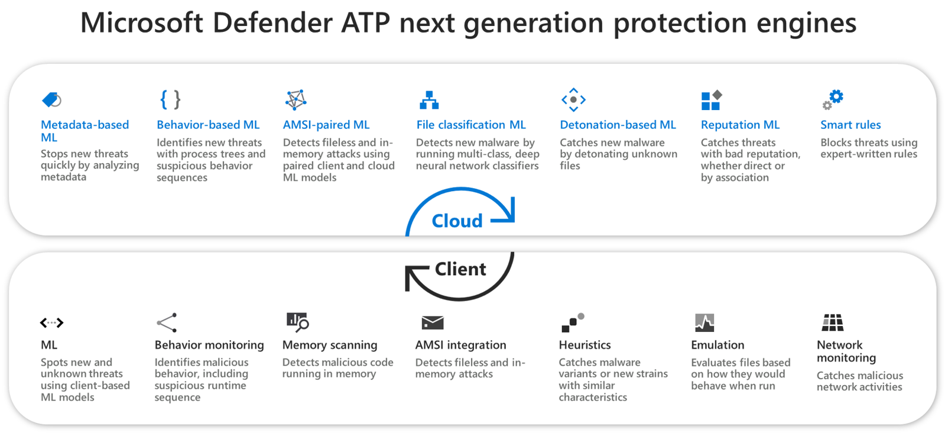
The most of us still run a Windows domain and have Endpoints with various operating systems. Windows uses the Microsoft Defender as antivirus. Additionally you can connect this to the opposite in the cloud, which is the Defender for Endpoint. This is an endpoint detection and response EDR/XDR product . Read more about this.
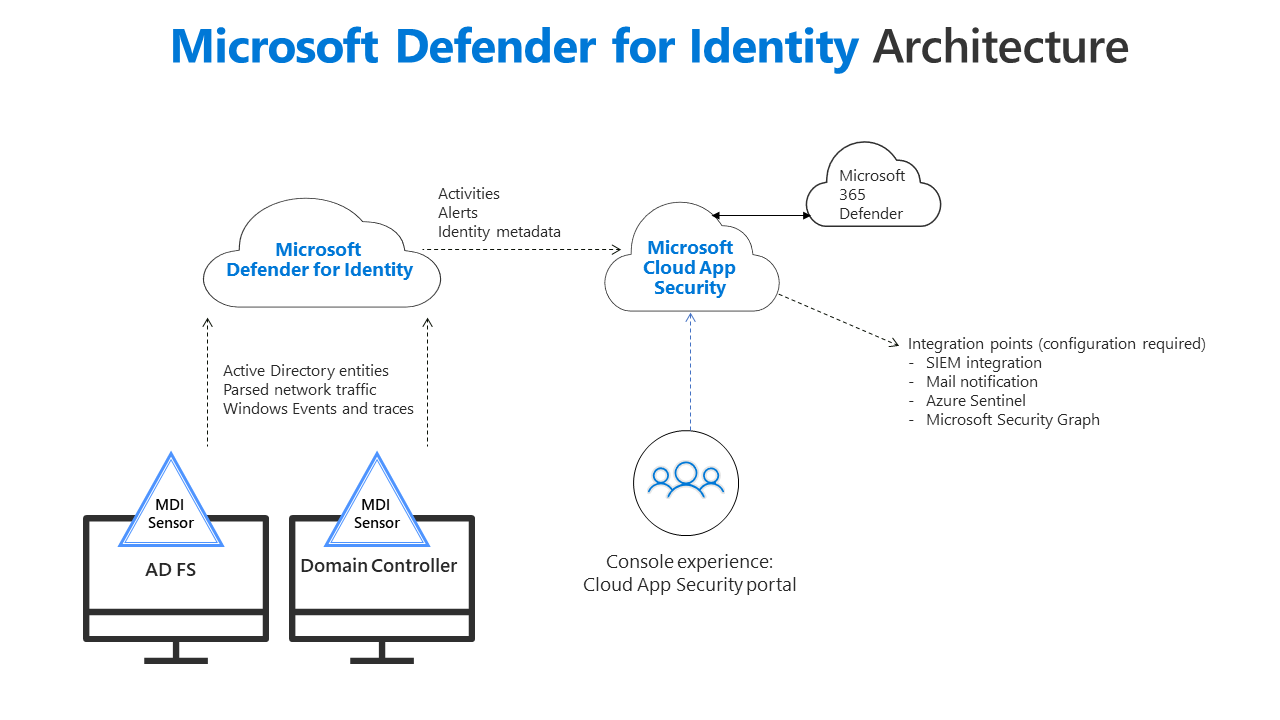
The second component we talk about is the Defender for Identity, which has an agent installed on the domain controller that observes domain activity. This product is effectively only to get more information about your Active Directory identities which will help you to detect if there are any suspicious actions. It is recommended to use this feature if the licenses are available. Read more about licensing.
The Internet
The Internet is a broad space that sources every resource imaginable. Collaboration with other organizations or cloud apps, is what we try to secure. Microsoft offers the following products to achieve this objective:
Microsoft cloud
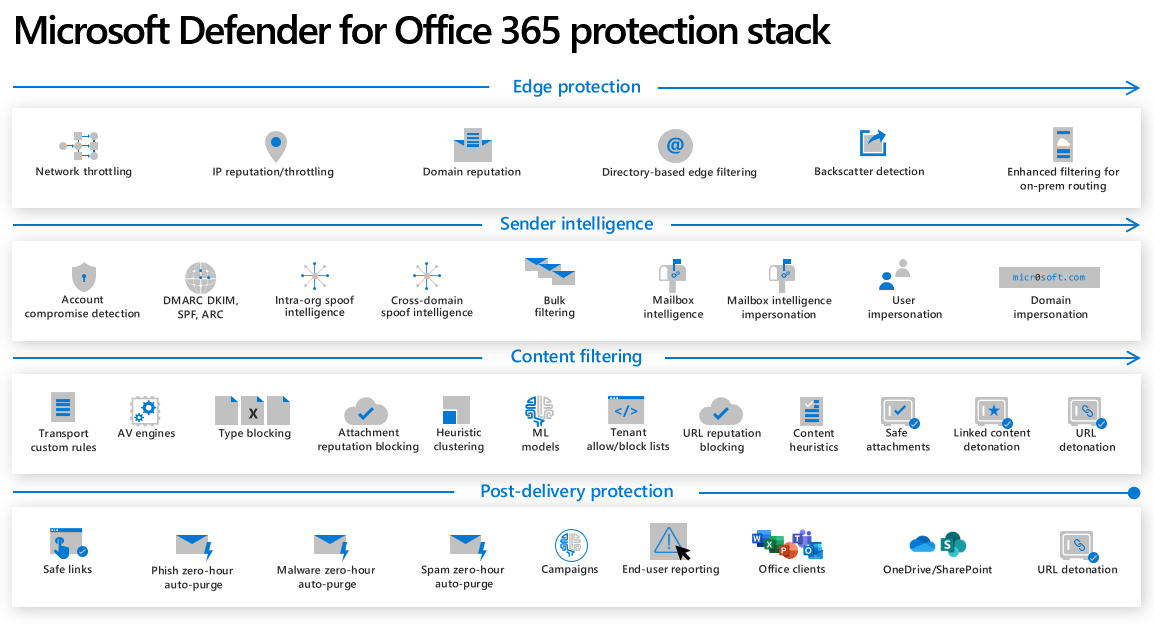
The Microsoft cloud is a multi-tenancy model, that houses more than 200 products and services. Each organization has a tenant that stores all the information. For example: Microsoft Entra ID, Intune Endpoint management, Microsoft Sentinel, Office 365 and so on. Defender for Office 365 protects web and office contents from the world wide web, which is the biggest attack surface. Configure spam and phishing policies, safe links and attachments to guarantee a high potential against threats.
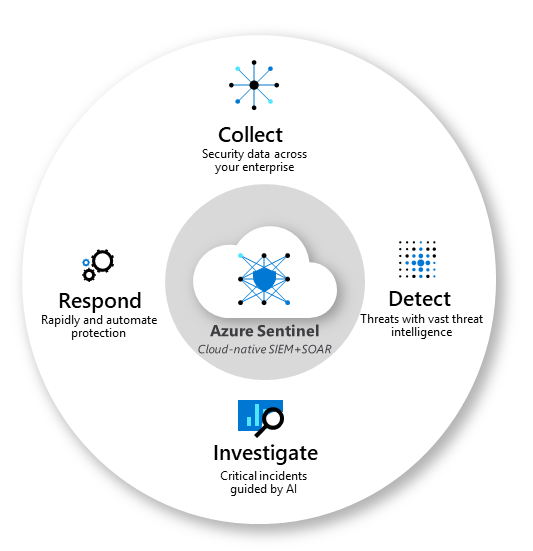
Microsoft Sentinel is a cloud-native security information event management (SIEM) solution, that is a central place for all security operations (SecOps). You can connect all of the mentioned products and services into this to get a better understanding of your security related data. Sentinel collects, detects, investigate and respond's to all kind of threats across the enterprise. Azure Log Analytics is the associated storage component.
Enterprise applications & registrations is the new way to unify identities across cloud applications available in the Internet. Each of those has a representative service principal in your tenant for more control.
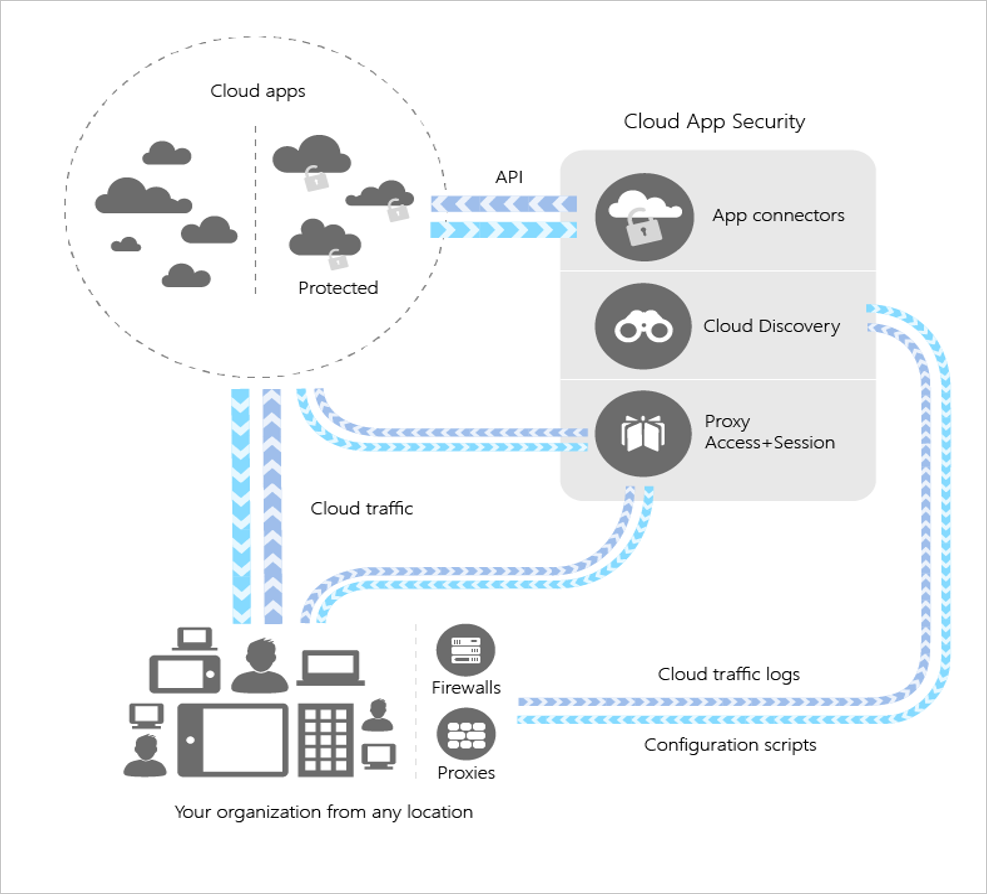
Defender for Cloud Apps is a product that monitors the traffic and behavior of the user to each of these Enterprise apps, often called cloud access security broker. It allows you to sanction over 16,000 specific applications from the web that Microsoft has information about security and compliance requirements.
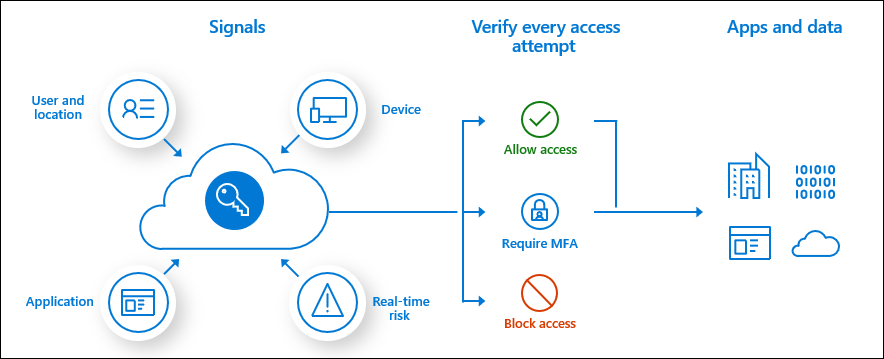
One of the most used components is Conditional access. The real benefit of it is, that you can connect it to nearly all of the other services to enforce a user action. The idea is simple; the user provides signals with each login, such as IP address, his device or the application he tries to log in. Then multiple actions can be set as required. MFA is clearly the most anticipated method to use in these situations. Allow or block access, require a password change, use an Entra hybrid joined device, use an approved client app are more controls to grant, if needed. Read more about Conditional access examples
Microsoft Defender XDR
- Defender for Endpoint
- Defender for Office 365
- Defender for Identity
- Entra ID Protection
- Defender for Cloud Apps
Microsoft Defender for Cloud
- Defender for SQL
- Defender vor VMs
- Defender for IoT
- Microsoft Sentinel
Learn more about Security:
 Niklas Tinner
 Niklas Tinner